Business continuity
Business Impact Analysis, continuity plan and backup checks, with the right questions already written and explained.
How long can you afford to be down? Better to know beforehand
The question "how long can we be down?" has a different answer for every business process. Finding out during an outage is the most expensive way to learn it.
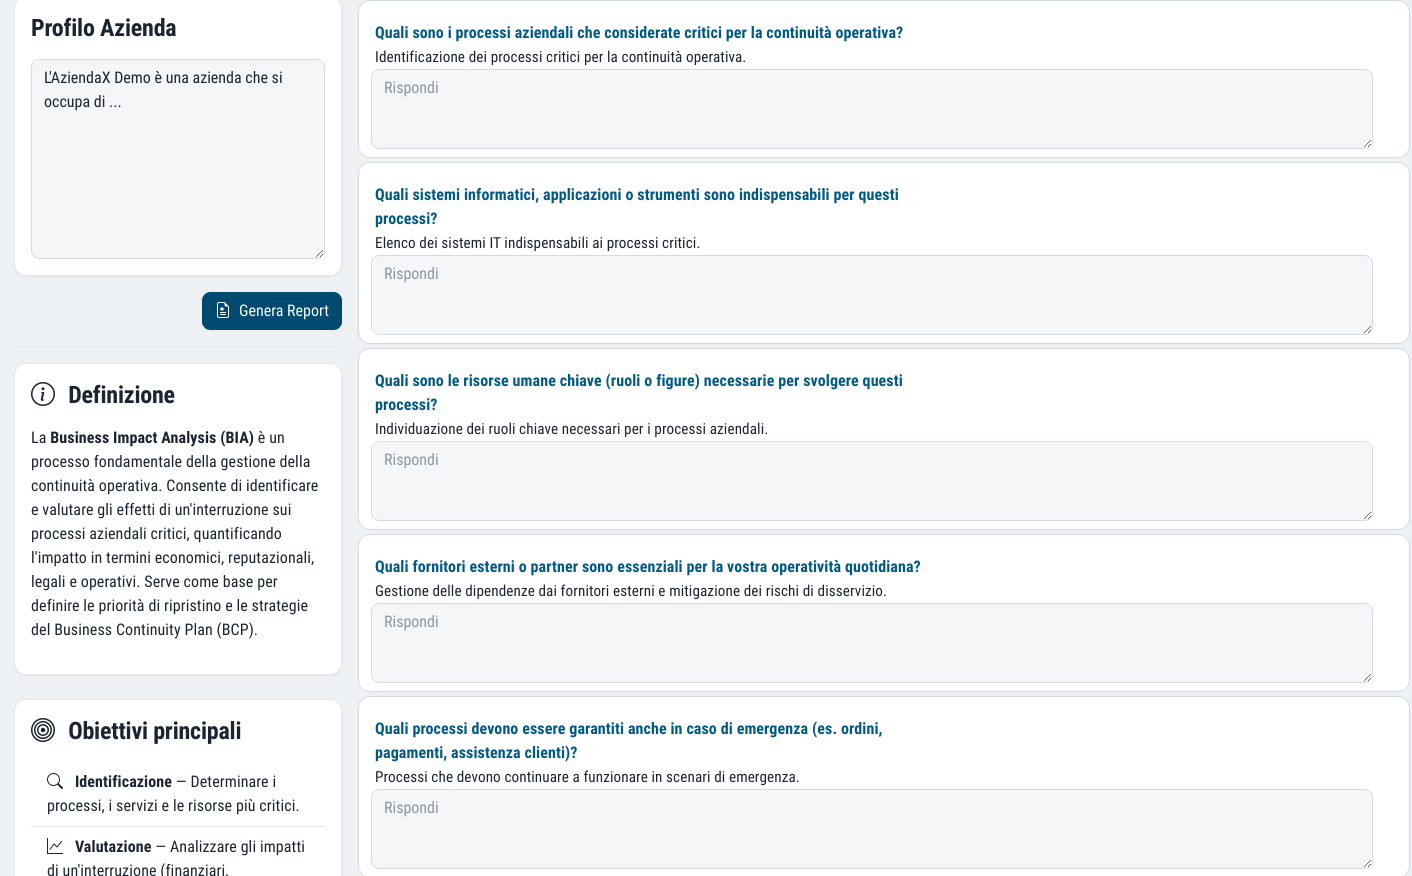
The three business continuity questionnaires lead the company to state it in advance: which activities are critical and how much disruption they can tolerate, how work carries on if a system is not available, and whether the backups have actually been tested or merely configured.
The questions are already written and explained, the answers are saved as you type, and at the end you can ask us for the document with a single button.
A backup that nobody has ever tried to restore is an assumption, not a continuity measure.
What you get
Three guided paths
Business impact, business continuity, backup and recovery: three questionnaires built on the same method.
Guidance next to every question
Every question has its own explanation and every questionnaire has a dedicated guidance panel.
Continuous saving
Answers are saved as you fill them in: stop and pick up again whenever you like, with no button to remember.
Document on request
At the end of the path you ask our team, with a single button, to produce the final document.
Business Impact Analysis, Business Continuity Plan, Backup & Recovery
Three documents that standards often require together, and that are best built in the same order.
Business Impact Analysis
Which processes are critical, how long they can remain down and what impact their interruption has. It is the basis for every later choice.
Business Continuity Plan
How work carries on if a system, a site or a supplier is not available: who does what, and with which alternatives.
Backup & Recovery
What is backed up, where, how often, and above all whether recovery has been tested and how long it took.
It starts with a description of the company
The first step is the company description. That description does not stay locked inside the questionnaire: it is reused by all the documentation. You write it once.
Then you fill in the three questionnaires in whatever order you prefer. The question catalogue is the same for all customers and is versioned; your answers stay in your environment.
- Questions with a title and description, already written
- A side guidance panel for each type of questionnaire
- Automatic saving while you fill it in
- Versioned question catalogue
- Company description shared with the other documents
- Request for the final document sent to support with one button
Business continuity in the standards
NIS2 includes business continuity, backup management and crisis management among its minimum security measures. ISO/IEC 27001 requires information security to be maintained during a disruption too, and DORA devotes an entire regulation to digital operational resilience.
Having a written Business Impact Analysis and continuity plan is not enough for all these standards, but without them none of them is met. The answers you give here become the basis for the documents and evidence in the Compliance module.
Extra help. If your staff have never written a continuity plan, the questionnaires are designed to be completed without a consultant at your side. If you would rather have someone with you, Dottor Marc's consulting works on the same data.
Questions about business continuity
What is the difference between a Business Impact Analysis and a Business Continuity Plan?
The Business Impact Analysis measures: it tells you which processes are critical and how long they can remain down. The Business Continuity Plan decides: it describes how work carries on when one of those processes is interrupted. Without the first, the second is written blind.
Do I have to fill everything in at once?
No. Answers are saved as you type, so you can stop and pick up again on different days, even with different people who know different departments.
Who writes the final document?
Once you have finished, you request the document with a button: the request goes to our support team, who work from the answers you have given.
Which standards it supports
Often activated together
Risk Assessment
Risk analysis based on ISO/IEC 27005, with a treatment plan and residual risk.
Learn more GovernIncident Response and Data Breach
CSIRT, incident handling phases and a breach register with notification deadlines.
Learn more GovernCompliance and GRC
Policies, procedures, audits and evidence for eight frameworks: one piece of work that counts for several standards.
Learn moreDo you know what someone looking for a target can see of your company?
In a demo on your real systems we show you what is exposed, how much it matters and where to start. Then, if you need it, a tailored proposal.