Incident Response and data breach register
Who does what when it happens, decided in advance. And the register of events, with the incident phases to follow and a name next to every action.
An incident is no time to improvise the organisation chart
Decisions about who coordinates, who communicates and who steps in should be made when there is time to make them, not with systems down. The incident response module starts from fifteen response roles already in place and asks you only to assign them to people in your organisation.
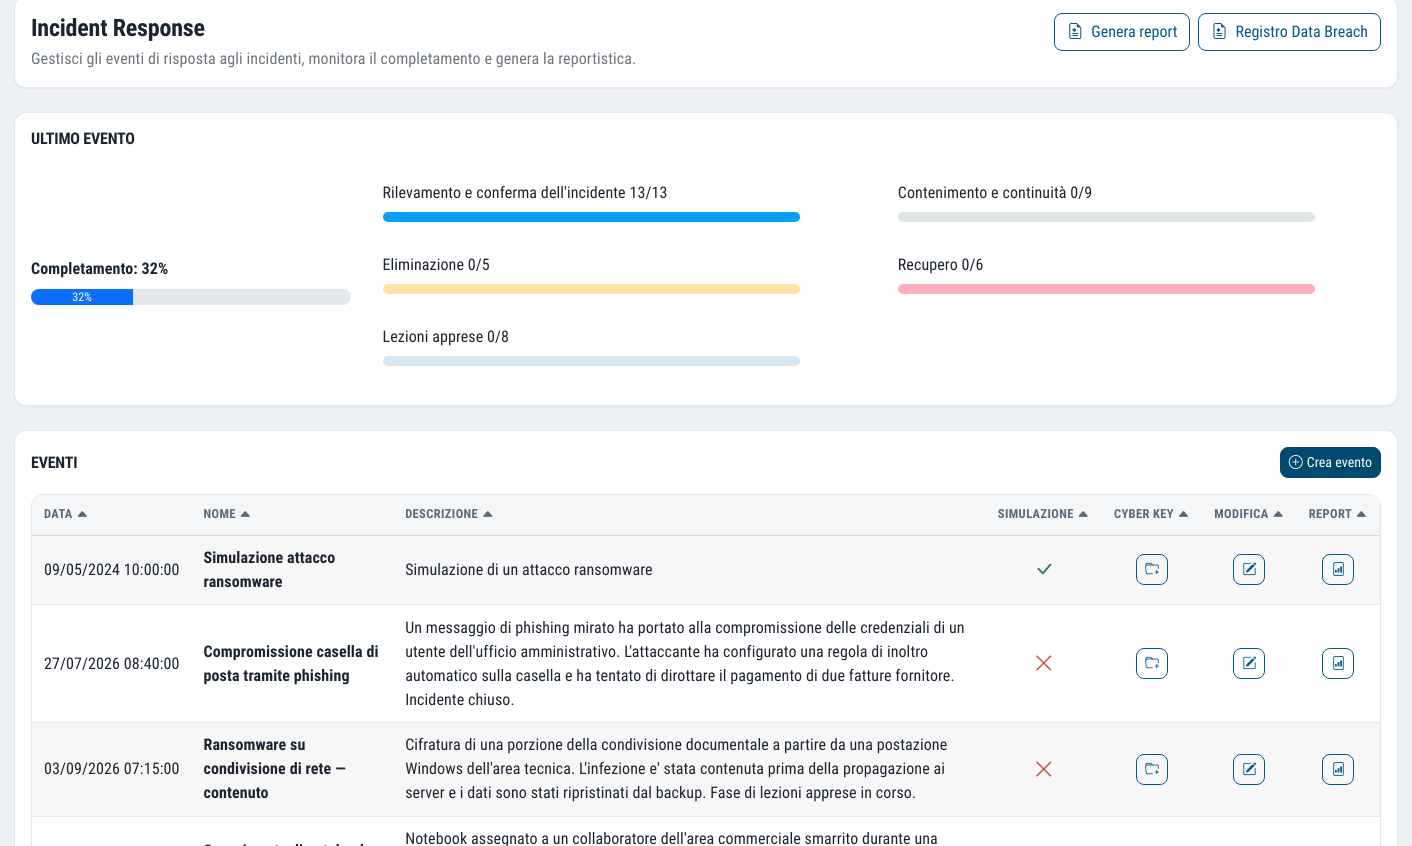
When an event occurs, the data breach register records it with the checklist of phases: prepare, detect, contain, eradicate, recover, learn. Every action has a name next to it and a status.
At the end, the PDF report documents what was done: it is what you need to report to the authority and to avoid repeating the mistake.
With the MDR + SOC levels, the incident has someone in charge and it is the provider: Dottor Marc takes on the role of Incident Response Team Lead.
What you get
Fifteen roles ready to use
Already created in every new Dottor Box and organised into sections: you assign one or more people to each.
The incident phases
A checklist for every event, with each item assigned to a member of the team.
You always know where you are
Completion percentage by phase and by event, while the incident is under way.
PDF reports
The CSIRT report and the report for each event, for notification and for your records.
The incident response team, filled in once
The CSIRT (Computer Security Incident Response Team) is the team that steps in when something goes wrong. In Dottor Box you assign one or more people from your staff directory to each of the fifteen roles and declare the single CSIRT contact, with email and phone number. The CSIRT PDF report documents how the team is made up.
The CSIRT directory is shared across modules: it supplies the assignees for compliance tasks, the owners in the Risk Assessment and those in the records of processing. You fill it in once and it applies everywhere.
Preparation and detection
What was ready and how the event was discovered.
Containment and eradication
Stopping the spread and removing the cause.
Recovery and lessons learned
Getting back to normal operations and writing down what to change.
Who leads the incident response
The module is the same. What changes is how much of the work we do, depending on the service level you choose.
| Aspect | Security Monitor | MDR + SOC | MDR + SOC 24/7 |
|---|---|---|---|
| Role in the incident | You lead, with our reports and alerts | Dottor Marc takes on the role of Incident Response Team Lead | As MDR + SOC, with round-the-clock availability |
| Who acts on alerts | Your team | Dottor Marc's SOC | Dottor Marc's SOC, at any time |
| Support | CSIRT with data breach register | 8/5 tickets, during business hours | Dedicated phone line 24 hours a day, 7 days a week |
Why it matters. At the MDR + SOC levels our SOC works with your CSIRT on reported incidents, classifies requests by urgency and severity, documents the actions taken and coordinates with external suppliers when needed. At 24/7 the team works to procedures already agreed and tested with you, so nobody has to invent them at the worst possible moment.
Data breach management and notification duties
The GDPR requires you to document every personal data breach, including those that do not have to be notified. NIS2 requires essential and important entities to notify significant incidents within tight deadlines. In both cases you need to know, with dates and names, what happened and what was done.
The event register and the PDF reports are that documentation. The Compliance module shows the data breach register as evidence against the clauses that require it.
- CSIRT report showing how the team is made up
- A report for each event, for notification and for your records
- Progress by phase always visible
- Someone responsible for every action on the checklist
Which standards it supports
Frequently asked questions about incident response and data breaches
How quickly must a cyber incident be notified?
It depends on the rules that apply. Under NIS2, as applied in Italy, a significant incident requires an early warning to CSIRT Italia, the Italian national CSIRT, within 24 hours, a notification within 72 hours and a final report within one month. Under the GDPR, a personal data breach must be notified to the Garante (the Italian Data Protection Authority) within 72 hours of discovery, if it poses a risk to the people concerned. Find out more in the guide data breach: what to do in the 72 hours.
What is a CSIRT?
It is the Computer Security Incident Response Team, the team that prepares and manages the response to incidents. In a company it is a group of people with defined roles: who coordinates, who decides, who communicates, who works on the systems. In Italy there is also the national CSIRT within ACN, Italy's National Cybersecurity Agency, which receives NIS2 notifications. CSIRT in the glossary.
Do data breaches that are not notified also have to be recorded?
Yes. Article 33 of the GDPR requires you to document every personal data breach, with the facts, its effects and the remedial action taken, even when notification is not required. This documentation lets the authority check the assessments you made.
Does an SME need an incident response plan too?
Yes, and it pays to write it beforehand. Deciding in advance who coordinates, who informs customers and authorities and who works on the systems reduces mistakes and lost time at the worst possible moment. NIS2 and ISO/IEC 27001 ask for it explicitly; the fifteen roles already set up in Dottor Box give you the outline to start from.
Can Dottor Marc handle the incident for us?
With the MDR + SOC levels our SOC receives the alerts, works with your CSIRT and Dottor Marc takes on the role of Incident Response Team Lead. With MDR + SOC 24/7 availability is round the clock, with a dedicated phone number. With Security Monitor your team leads the response, with the platform's reports and alerts. SOC and MDR.
Often activated together
Cyber Agent
The endpoint agent: security events, file integrity and clear, readable alerts.
Learn more GovernBusiness continuity
Business Impact Analysis, continuity plan and backup checks, guided by questionnaires.
Learn more GovernCompliance and GRC
Policies, procedures, audits and evidence for eight frameworks: one piece of work that counts for several standards.
Learn moreDo you know what someone looking for a target can see of your company?
In a demo on your real systems we show you what is exposed, how much it matters and where to start. Then, if you need it, a tailored proposal.