Threat Intelligence
The security news that concerns you, not everything else.
Following threats is nobody's job
Every day dozens of news items are published about vulnerabilities, attacks and compromised suppliers. Following them all is a full-time job, and in most companies nobody does it: the news that matters arrives late, or not at all.
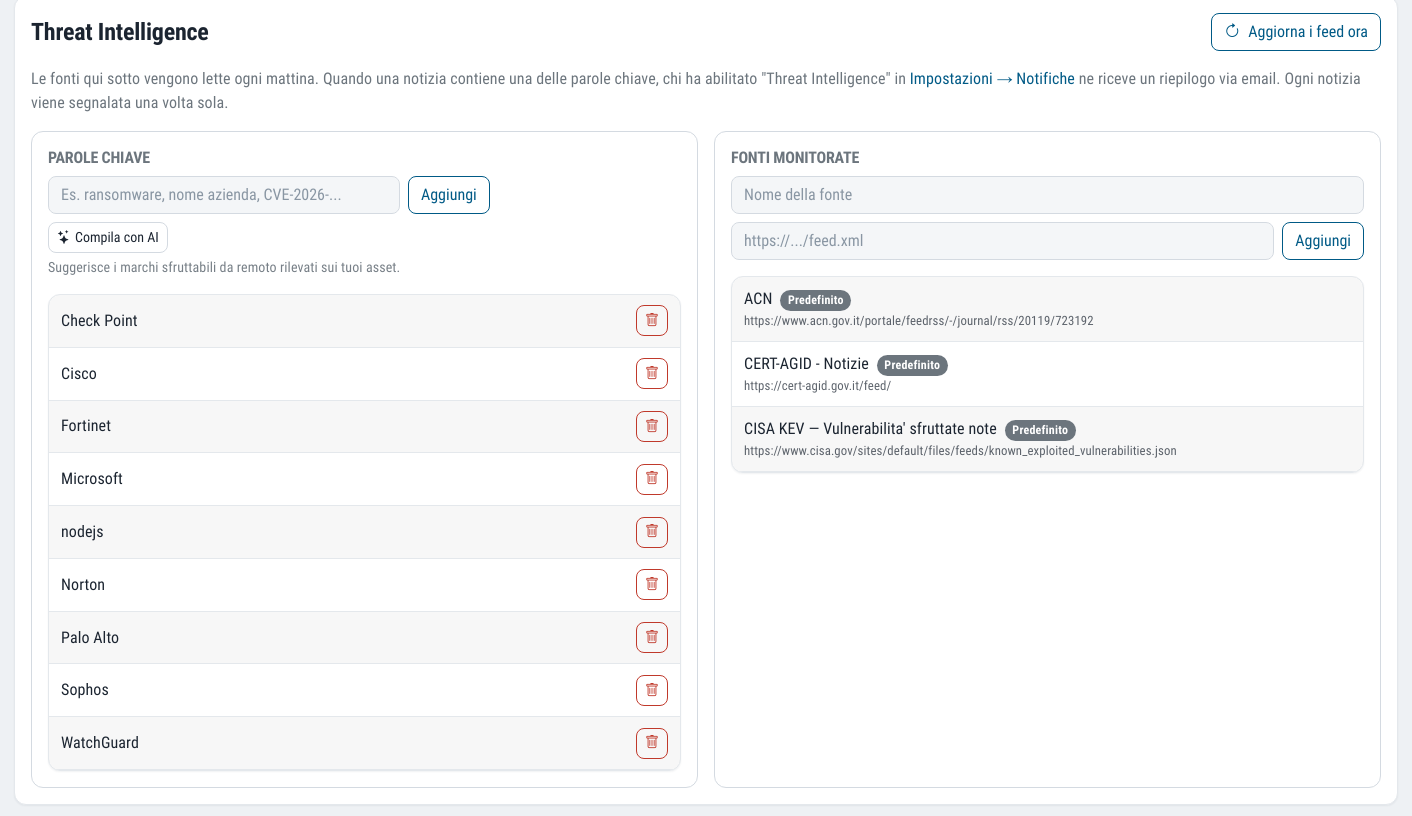
The Threat Intelligence module does it for you. Every day it reads cyber security sources and writes to you only when something appears that concerns you: the software you use, the supplier you depend on, the technology your business system runs on. Everything else stays out of your inbox.
One news item, one email. The history of matches recognises every article, and you are never notified of the same news twice.
What you get
Chosen sources
Predefined security sources, plus the RSS or Atom feeds you add yourself.
Your keywords
Products, suppliers and technologies you use: they decide what is of interest to you.
A digest, when it is needed
A summary by email only when there is a real match, not a daily newsletter.
No duplicates
Each news item is notified only once, and the history remains available.
From security sources to your inbox
Choose the sources
Start from the predefined sources and add the feeds you already follow: your supplier's blog, a manufacturer's bulletin, an industry portal.
Enter the keywords
The names of the software, suppliers and technologies you use. If you do not know where to start, assisted completion suggests a first list.
Reading happens daily
Every morning the platform reads the sources and compares the headlines with your keywords. You can also refresh straight away with one click.
Receive the digest
When there is a match, an email goes to the recipients who have chosen to receive it in the notification settings.
When the news concerns your supplier
The manufacturer of the firewall at your premises publishes an advisory on an actively exploited vulnerability. The same day the news appears in security sources. If the product name is among your keywords, the next morning you have the article in your inbox, without having had to look for it.
From there you can check with the vulnerability assessment whether your systems are exposed, and document what you have done.
- Custom feeds in addition to the predefined ones
- Keywords you can change at any time
- Matching on the article headline, to reduce false alarms
- Recipients chosen by opt-in in the notification settings
- History of matches kept, with no duplicates
Threat intelligence: what to know before activating it
Which keywords should I enter?
The names of the products you really use (firewall, VPN, business system, email system), of the suppliers you depend on and of the technologies your day-to-day work relies on. A few precise words are better than many generic ones: every word that is too common brings news you do not need.
Can I add the sources I already follow?
Yes. As well as the predefined sources you can enter any RSS or Atom feed: a manufacturer's bulletin, a CERT's blog, an industry portal.
Who receives the emails?
Only the people who have turned on the notification in their own settings. Those who are not interested receive nothing, and those who are receive a digest rather than one email per article.
How is it different from Dark Web Monitoring?
Threat Intelligence reads public security sources and alerts you about software, suppliers and technologies. Dark Web Monitoring, on the other hand, looks for company credentials in data breaches and for the company name on ransomware leak sites. The two complement each other.
Which standards it supports
Gathering threat intelligence is an explicit control in ISO/IEC 27001:2022 and part of the risk management required by NIS2 and DORA, including along the supply chain.
Often activated together
Dark Web Monitoring
Compromised company credentials and mentions of your brand on leak and ransomware sites.
Learn more GovernSupply Chain
Supplier assessment with questionnaires completed from a link, no accounts needed.
Learn more SeeVulnerability Assessment
Six checks from inside and outside, with CVSS severity, history and alerts on what is new.
Learn moreDo you know what someone looking for a target can see of your company?
In a demo on your real systems we show you what is exposed, how much it matters and where to start. Then, if you need it, a tailored proposal.