Google Workspace, your security posture
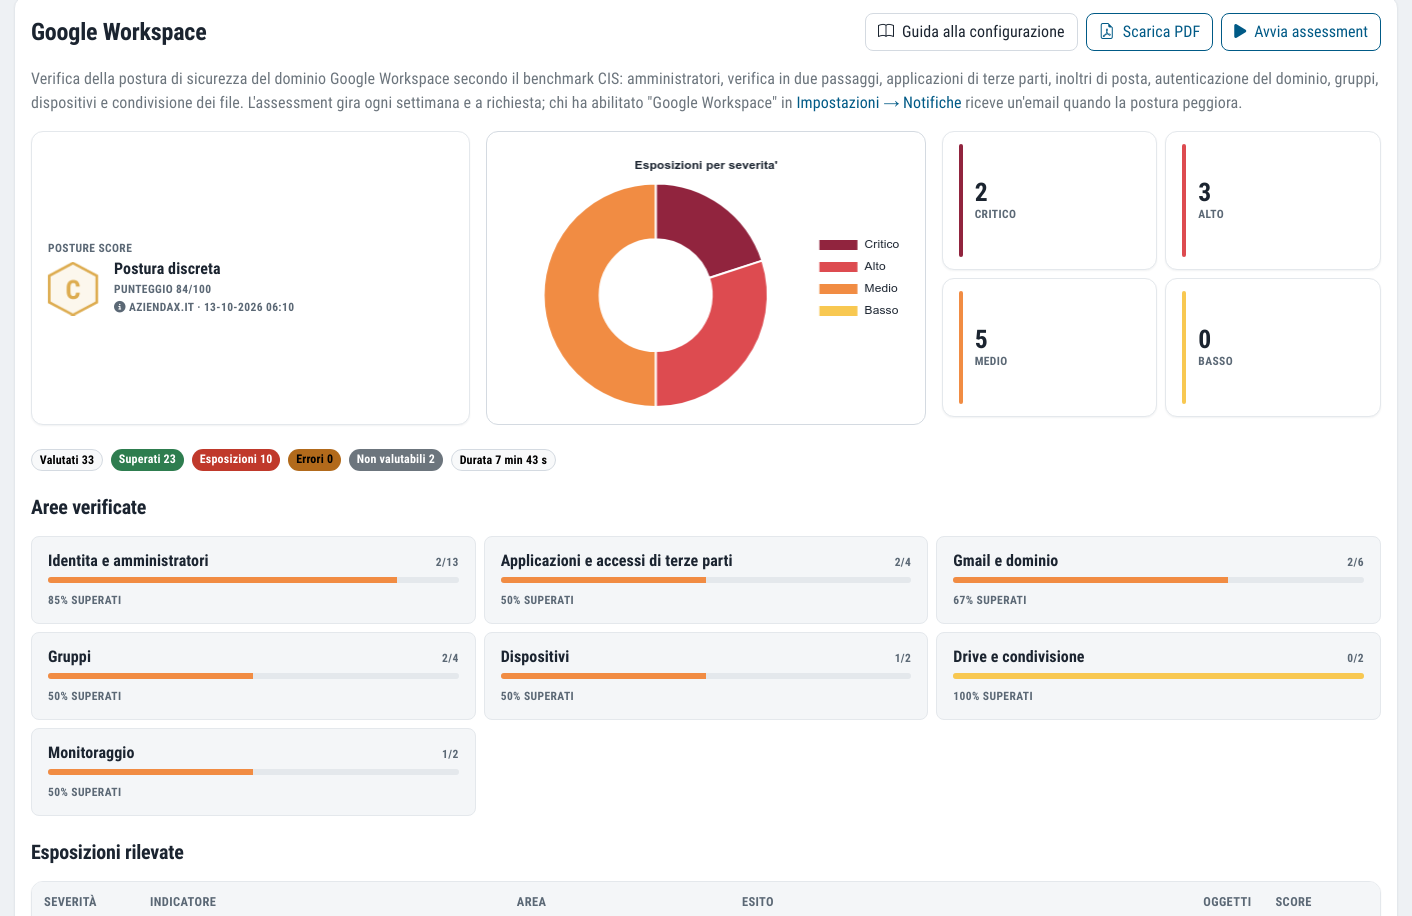
35 checks from the CIS Google Workspace Foundations catalogue, with the same scoring method used for Microsoft 365.
The settings nobody reviews after activation
Google Workspace security comes down to a handful of settings that almost nobody checks again after day one: 2-Step Verification not enforced, less secure apps still allowed, unrestricted file sharing outside the organisation, groups open to anyone.
Dottor Box checks them all with 35 indicators taken from the CIS Google Workspace Foundations catalogue, the public reference for configuring the platform securely. A score tells you how far you are from the recommended configuration and, above all, where to act first.
The calculation method is the same as for the Microsoft Entra ID assessment: if Google and Microsoft coexist in your company, the two scores can be set side by side.
When Google does not provide a piece of data, the indicator shows as "not assessable", not "passed". A check that was never carried out is not passed off as successful.
What you get
Weekly check
Identities, third-party apps, Gmail, groups, devices and sharing, checked against the CIS catalogue.
Your domain against spoofing
SPF, DKIM and DMARC checks: who can send email pretending to be your company?
Exfiltration routes
Automatic forwarding outside the organisation and mailbox delegation, the classic ways email leaves without anyone noticing.
A comparable score
The same method as Microsoft Entra ID: useful if you use both platforms.
Seven CIS control areas
The 35 indicators are grouped by area: the score for each one tells you where the problem lies.
- Identities and administrators: 2-Step Verification, privileged accounts
- Third-party applications and access connected to the company account
- Gmail and domain: SPF, DKIM, DMARC, forwarding and delegation
- Groups: who can join and who can post
- Devices that access company data
- Sharing of files and folders outside the organisation
- Monitoring: alerts and logs enabled in the console
A service account, with permissions explained one by one
The in-product guide, in Italian and English, takes your administrator from the Google Cloud console to the first report.
Create the service account
In your Google Cloud project you create a service account, enable the required APIs and upload the key to Dottor Box, where it is stored encrypted.
Authorise delegation
Dottor Box shows you the client ID and the exact scopes to paste into the Admin console. The guide explains what every single permission requested is for.
The check runs every week
The analysis starts on Tuesday morning, on a different day from the Microsoft one so that two long processing jobs do not overlap. You can also start it whenever you like.
Read-only, in practice. The scopes requested are read-only, with three exceptions for which Google offers no read-only variant. Even on those, the platform only performs reads: it does not change users, groups or settings.
SPF, DKIM and DMARC read where they actually live
No Google API exposes the email authentication records. That is why Dottor Box reads them directly from your domain's DNS, as a mail server receiving one of your emails would. The result is what the world sees, not what the console says.
"Not assessable" does not mean "passed"
Sometimes Google does not populate a field, because of the licence or a setting that has never been touched. In that case the indicator is marked not assessable and you see it as such. Many tools, when the data is missing, count the check as passed: it is the quickest way to raise a score and the surest way to be caught unprepared at an audit.
Which standards it supports
The CIS catalogue is the technical basis of many frameworks: the results become evidence for access control, email protection and configuration management.
Frequently asked questions about Google Workspace security
What are SPF, DKIM and DMARC, and why do they matter?
They are three DNS records that tell mail servers who may send email on behalf of your domain and how to handle messages that fail the check. Without them, it is easy to send emails that appear to come from your company. Since 2024 Google and Yahoo have required them from anyone sending large volumes of email to their mailboxes.
Do you need a Google Workspace administrator to activate the check?
Yes. To authorise domain-wide delegation in the Admin console you need a super administrator account, and to create the service account you need access to a Google Cloud project. The in-product guide takes whoever has these permissions through it step by step.
What is the CIS Google Workspace Foundations catalogue?
It is the set of recommendations for configuring Google Workspace securely, published by the Center for Internet Security, the non-profit organisation that also maintains the CIS Controls. Dottor Box uses 35 of its indicators, grouped into seven areas.
Does the check also work with a personal Gmail account?
No. The check concerns a Google Workspace domain, because it relies on the Admin console and domain delegation, which personal Gmail accounts do not have. If someone uses a personal mailbox for work, that is a risk to be dealt with separately.
How often is the check repeated?
Every week, on Tuesday morning, and at any time with a manual start. So you can track the score over time and see whether your fixes have taken effect. If you also use Microsoft 365, the Microsoft Entra ID check runs on Monday.
Often activated together
Microsoft Entra ID
The security posture of your Microsoft 365 tenant across 72 indicators, read-only.
Learn more SeeAccess logs
System administrator logins collected and retained as the Italian Data Protection Authority requires.
Learn more SeeDark Web Monitoring
Compromised company credentials and mentions of your brand on leak and ransomware sites.
Learn moreDo you know what someone looking for a target can see of your company?
In a demo on your real systems we show you what is exposed, how much it matters and where to start. Then, if you need it, a tailored proposal.