Supply Chain
Assess the security of your suppliers with a questionnaire they complete from a personal link, without registering.
The problem is not writing the questionnaire, it is getting it completed
NIS2 and ISO/IEC 27001 require you to know whether your suppliers are secure, and the checking falls to you. In practice that means sending questionnaires by email, getting files back in ten different formats and chasing those who do not reply.
With the Supply Chain module the supplier receives a personal link, opens a page and answers when they have time: the work is saved as they go. They attach the documents you ask for and confirm submission. They do not have to create an account.
You see how far each one has got without sending reminders blindly, and the answers stay on record with their evidence.
The fewer steps you ask of a supplier, the more answers you get. That is why a link is all it takes: no registration, no password.
What you get
Questionnaires you can build
Organised by supplier category, with questions you create from scratch or duplicate from existing ones.
Send to one or to all
Each supplier receives their personal link to the questionnaire by email.
No account
The supplier completes it from the link, saves answer by answer and attaches the evidence.
Status always visible
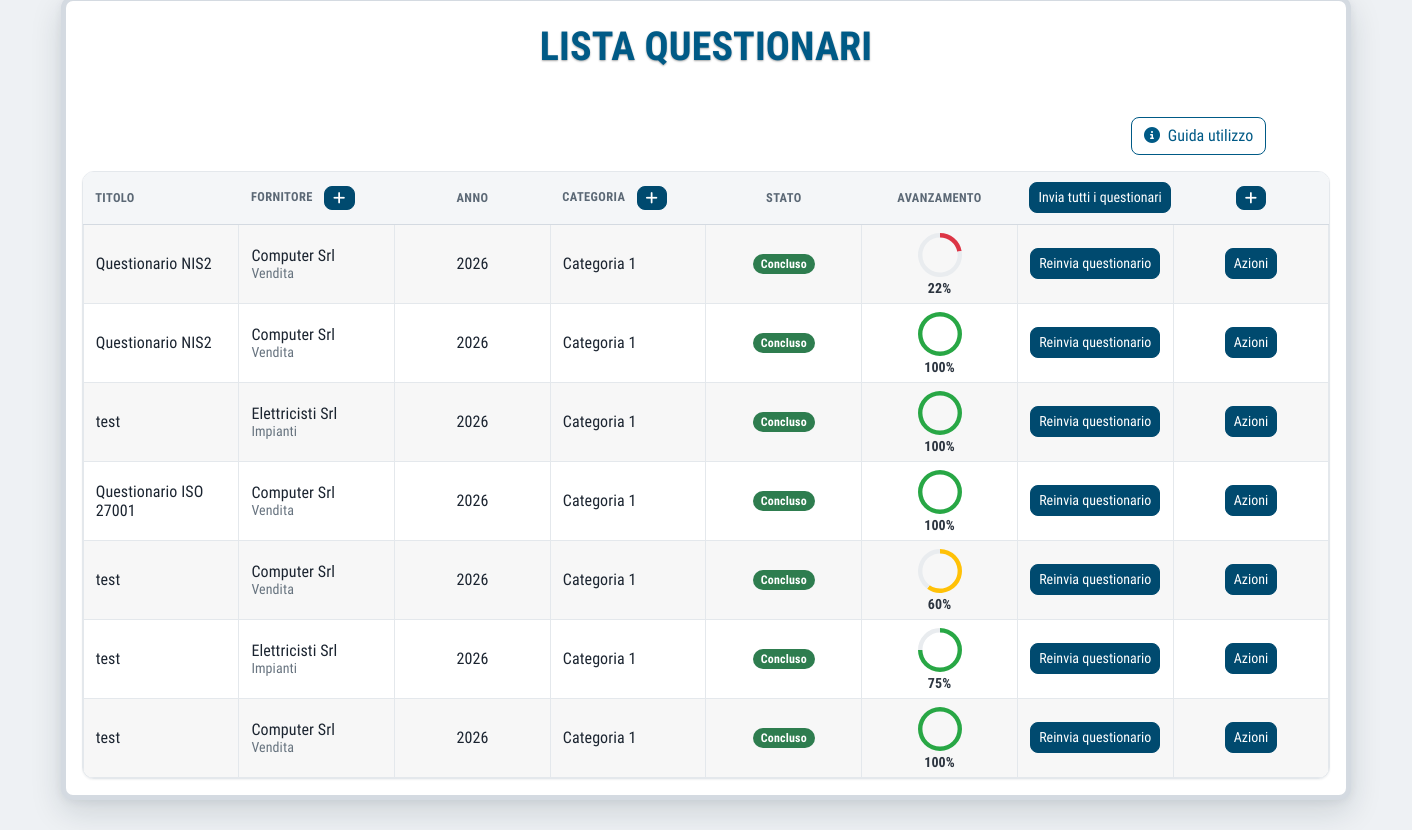
Completion percentage and status of every questionnaire, without having to ask.
Supplier assessment in four steps
Organise your suppliers
Enter your suppliers and define the questionnaire categories: whoever handles your data should not be assessed in the same way as whoever delivers your stationery.
Build the questionnaire
Create the questions or duplicate those you already have, and adapt the questionnaire to the category.
Send it
To a single supplier or to all of them, by email, with a personal link for each.
Read the answers
Answers and attached evidence stay in the platform, with the status of every questionnaire.
What the recipient of the questionnaire sees
A single page, reached from the link received by email. The supplier can stop and pick up again: every answer is saved as soon as it is written.
- Completion without creating an account
- Saving answer by answer
- Attachments as evidence for the answers
- Explicit confirmation of submission
- A request for the PDF report or to be contacted
How far each supplier has got
For each questionnaire you see the completion percentage and the status: not started, in progress, completed. You know who needs a reminder and who does not.
The answers can be viewed with the attached evidence, and the questionnaire report can be given to the supplier as the outcome of the assessment.
Supply chain security in the standards
NIS2 includes supply chain security among the risk management measures that essential and important entities must adopt. ISO/IEC 27001 devotes several controls to supplier relationships, and DORA requires the financial sector to govern the risk from ICT providers.
They all ask for the same thing: that you asked, that the supplier answered, and that you can prove it. The questionnaire with its evidence is that proof, and the Compliance module links it to the requirements of the standards.
With the MDR + SOC levels Dottor Marc also works with your suppliers and partners on supply chain security, as well as giving you the tool to assess them.
Questions about the supply chain
Does the supplier have to register with Dottor Box?
No. They receive a personal link by email and complete the questionnaire from there, without creating an account and without a password to remember.
Can I use different questionnaires for different suppliers?
Yes. Questions are organised into questionnaire categories, so a supplier that processes your data receives different questions from one that delivers your office supplies.
What stays on record?
The supplier's answers, the evidence they attached and the status of the questionnaire. It is the documentation the standards require to show that you have assessed your supply chain.
Which standards it supports
Often activated together
Risk Assessment
Risk analysis based on ISO/IEC 27005, with a treatment plan and residual risk.
Learn more GovernGDPR forms
Appointments, privacy notices and authorisation letters for all your staff, generated in one step.
Learn more GovernCompliance and GRC
Policies, procedures, audits and evidence for eight frameworks: one piece of work that counts for several standards.
Learn moreDo you know what someone looking for a target can see of your company?
In a demo on your real systems we show you what is exposed, how much it matters and where to start. Then, if you need it, a tailored proposal.